The five pillars of an AML compliance program, officer, controls, testing, training, due diligence, and the gaps regulators look for.
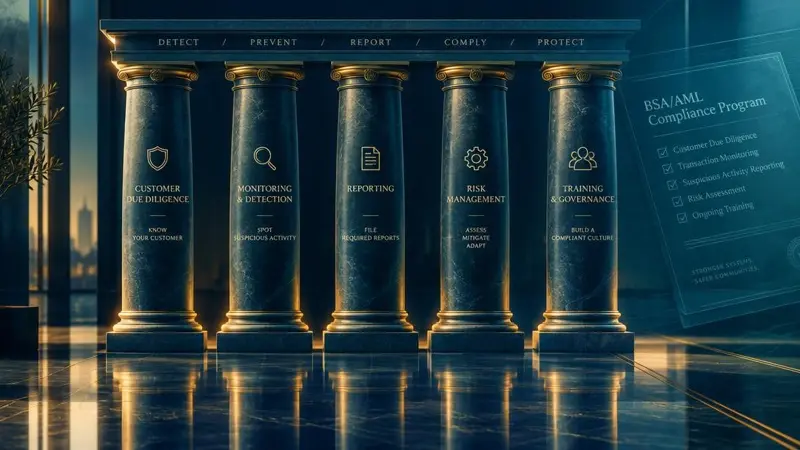
A complete BSA/AML program rests on five pillars: a designated compliance officer, internal controls, independent testing, ongoing training, and customer due diligence
A complete BSA/AML compliance program rests on five pillars: a designated compliance officer, internal controls, independent testing, ongoing training, and customer due diligence. Regulators expect all five to be documented, current, and tailored to the risks a business actually faces, not simply present on paper. When one pillar is missing or out of date, the others weaken, and the gaps tend to surface quickly during an examination or a banking-partner review.
Regulators expect all five pillars to be documented, current, and proportionate to the business's actual risk profile
The Five Pillars of an AML Compliance Program
These five elements are widely recognized as the foundation of an effective BSA/AML program. The exact requirement varies by institution type, a bank, a money services business, a mortgage lender, and a fintech may each be covered by different rules, but the pillars themselves are the same building blocks examiners and auditors look for across regulated industries.
Examiners test whether each pillar works in practice, not just whether it exists on paper
1. A Designated BSA/AML Compliance Officer
A named, qualified person is responsible for the day-to-day administration of the program, owning the risk assessment, overseeing monitoring and reporting, and keeping policies current. The officer should have the authority, resources, and access to leadership needed to make the program effective. A program that exists only on paper, with no one accountable for running it, rarely holds up under scrutiny.
The most common gaps are stale policies, missing independent testing, untracked training, and incomplete due diligence
2. Internal Controls
Internal controls are the written policies, procedures, and systems that put the program into practice: customer identification, transaction monitoring, recordkeeping, suspicious activity reporting, and escalation workflows. Good controls are specific to the business, they describe what staff actually do, and they are reviewed and updated as products, customers, and risks change. Generic, copy-and-paste policies are one of the clearest warning signs of a weak program.
Independent testing must be performed by someone genuinely independent of the AML function
3. Independent Testing
Independent testing is a periodic, objective review of the program by someone who is not involved in running it. Its purpose is to confirm that policies are actually followed, that monitoring is calibrated to the business's risks, and that the program works in practice, not just on paper. The reviewer must be genuinely independent of the AML function; a self-review by the compliance officer does not satisfy the expectation. Businesses that do not perform independent testing internally should understand that it is a distinct requirement, separate from the day-to-day operation of the program, and should plan for it accordingly.
Training matters most when it is role-appropriate, recurring, and tracked with completion records
4. Ongoing Training
Employees are the front line of any compliance program, and training is how they learn to recognize red flags, follow procedures, and escalate concerns. Training should be delivered on a recurring basis, be appropriate to each person's role, and, critically, be tracked. Regulators routinely ask not only whether training happened but who completed it and when. Training that is delivered but never documented is hard to demonstrate during an examination.
Strengthen a program by starting with a real risk assessment, documenting policies, training and tracking staff, and reviewing on a schedule
5. Customer Due Diligence
Customer due diligence (CDD) means knowing who your customers are and understanding the risk they present. That generally includes verifying identity at onboarding, taking a risk-based approach to ongoing monitoring, and, for legal entity customers, identifying beneficial owners where the rules require it. The depth of review should be proportionate to the risk: a simple, low-risk relationship calls for less than a complex one involving high-risk activity, geography, or products.
Soflo Consulting supports each pillar through its risk assessment service, its policy creation service, and its AML training center
Why the Pillars Matter: What Examiners and Auditors Look For
Examiners and auditors are not only checking whether each pillar exists, they are testing whether it works. In practice, that means asking whether the risk assessment reflects the business's real risk profile, whether the controls described in the policy match what staff actually do, whether training records show who completed what and when, and whether monitoring produces information specific enough to be useful. A program that answers "yes" to every procedural question but cannot demonstrate effectiveness is a program that will draw criticism.
The pillars also reinforce one another. A strong risk assessment tells you where to focus monitoring and training. Current training produces better alerts. Well-written controls make independent testing meaningful. When one pillar is neglected, the weakness tends to surface in the others.
The Most Common Gaps
When we review BSA/AML programs, the same weaknesses appear repeatedly, regardless of industry:
- Stale policies. Written procedures that were created once and never updated as the business added products, customers, or markets.
- Missing independent testing. Programs where no one outside the AML function has ever reviewed whether the controls actually work.
- Untracked training. Employees who were trained informally, with no records showing completion dates or attendees.
- Incomplete due diligence. Onboarding that collects an ID but never establishes a risk rating or a baseline of expected activity.
- A generic risk assessment. A document that rates everything "medium" without showing how the conclusion was reached.
- Undocumented decisions. Alert reviews, escalation decisions, and program changes that happened but were never written down.
None of these gaps require bad faith, they usually come from a program that was built once and never revisited as the business grew.
How to Build or Strengthen Your Program
Strengthening a BSA/AML program means tying each pillar back to something concrete and documented. In practice, that usually starts with three activities.
Start with a real risk assessment
Every other pillar depends on knowing where your risk actually is. A working risk assessment identifies your products, customers, geographies, and delivery channels, assigns risk levels with reasoning, and points to the controls that address the highest risks. A structured BSA/AML risk assessment service reviews an existing assessment and returns a written gap analysis with prioritized recommendations, a useful first step before you invest in policy or monitoring changes.
Document your policies and procedures
Written policies are the backbone of the internal controls pillar. They should describe what your staff actually do, customer identification steps, monitoring rules, escalation and reporting procedures, and recordkeeping, and they should be reviewed on a schedule rather than left untouched for years. Where a business does not yet have a written program, an AML policy creation service can build one from scratch around the business's specific risks.
Train and track your team
Training is the pillar most often delivered but least often documented. Role-appropriate content, delivered on a recurring cycle and recorded with completion dates, turns training into evidence rather than an assertion. A structured program such as Soflo's AML training center pairs the course content with the certificate tracking examiners ask for.
Review and keep it current
Finally, treat the program as something that changes with the business. Set a review cadence for the risk assessment and the policies, confirm that independent testing is performed by a genuinely independent party where your institution is required to have it, and retrain when products, people, or rules change. Programs that are built once and shelved almost always show their age by the next examination.
Where to Start
If you are building a program from scratch or tightening one that has drifted, the pillars give you a checklist: officer, controls, testing, training, and due diligence, each documented and current. Soflo Consulting combines online training, certificate tracking, policy review, risk assessment support, and practical guidance for regulated businesses across all 50 states. If you would like to see where your program stands today, the BSA/AML risk assessment service is a practical first step.
Disclaimer: This article is provided for general educational and informational purposes only and is not legal, financial, or regulatory advice. Requirements vary by institution type and jurisdiction, and rules change over time. Consult qualified legal and compliance professionals regarding your specific circumstances.
Frequently Asked Questions
The five pillars are a designated compliance officer, internal controls, independent testing, ongoing training, and customer due diligence. Together they form the foundation of a BSA/AML program, and regulators expect all five to be documented, current, and tailored to the risks the business actually faces. The specific rules that apply vary by institution type, but the pillars themselves are the same building blocks examiners and auditors look for across regulated industries.
What Is an AML Program and Who Needs It in 2026?
The foundational overview of BSA/AML program requirements, and how to tell whether your business is covered in the first place.
What Is Customer Due Diligence (CDD)?
How the due diligence pillar works, identity verification, risk rating, and beneficial ownership for legal entity customers.
What Is a Suspicious Activity Report (SAR)?
How the controls pillar turns monitoring into reporting, when a SAR is filed and what a good filing looks like.
Tags
AML/BSA Compliance Insights Team · Soflo Consulting
Soflo Consulting Team publishes BSA/AML compliance analysis for regulated businesses across the United States. The team covers regulatory enforcement actions, FinCEN guidance, risk assessment, and emerging compliance obligations for banks, money services businesses, mortgage lenders, fintechs, and other covered institutions.
8 sections
Key Takeaways
- 1A complete BSA/AML program rests on five pillars: a designated compliance officer, internal controls, independent testing, ongoing training, and customer due diligence
- 2Regulators expect all five pillars to be documented, current, and proportionate to the business's actual risk profile
- 3Examiners test whether each pillar works in practice, not just whether it exists on paper
- 4The most common gaps are stale policies, missing independent testing, untracked training, and incomplete due diligence
- 5Independent testing must be performed by someone genuinely independent of the AML function
- 6Training matters most when it is role-appropriate, recurring, and tracked with completion records
- 7Strengthen a program by starting with a real risk assessment, documenting policies, training and tracking staff, and reviewing on a schedule
- 8Soflo Consulting supports each pillar through its risk assessment service, its policy creation service, and its AML training center
Need Expert Guidance?
Put these insights into action. Talk to a compliance professional at Soflo Consulting compliance specialist.
Stay Ahead of Compliance
Get FinCEN updates, BSA/AML guidance, and federal compliance news delivered to your inbox - no fluff.